



The role of virtual patching has expanded far beyond its early days as a quick WAF or IPS ruleset designed to block known exploits. Modern virtual patching now operates closer to the workload—often at runtime—to neutralize malicious behavior before a vulnerability can be weaponized.
This evolution has been driven by two converging realities: the speed at which attackers exploit newly disclosed flaws, and the growing complexity of enterprise environments that makes instant patch deployment nearly impossible.
Recent data underscores the urgency. Verizon’s 2025 Data Breach Investigations Report shows that exploitation of vulnerabilities in internet-facing edge devices has surged from just 3% to 22% of breaches in a single year, with a median remediation time of 32 days.
Even with mature vulnerability management programs, many organizations only fully remediate about half of impacted systems in that time frame. Add the pressure of CISA’s Known Exploited Vulnerabilities (KEV) list—often accompanied by 24-hour patch deadlines—and it’s clear why virtual patching has become a default first response for security teams.
In this environment, virtual patching is no longer just a tactical stopgap. It’s a strategic control that can keep high-value systems secure during the window between vulnerability discovery and full remediation—especially when paired with a preemptive cyber defense model that blocks exploit attempts before they succeed.
Virtual Patching Has Never Been More Critical
When an organization’s IT suite gets beyond a certain level of complexity, unpatched vulnerabilities are inevitable. Cybercriminals know this—the majority of ransomware attacks exploit unpatched vulnerabilities.
Traditional patching took time, cost money, and couldn’t scale. With a traditional approach, on average, teams spent over 20 minutes of manual effort per individual vulnerability to detect, prioritize, and remediate it.
Yet even with all of this time spent patching, patch lag (the delay between patch release and deployment) remained high. Taking months, and in some cases, such as patching a medical device, it could still take years to deploy a patch.

Ironically, sometimes you can patch too fast. One of Morphisec’s clients, Motorola CISO Richard Rushing, told us that taking an aggressive approach to patch management puts him ahead of the vendors he uses. By the time he had patched thousands of endpoints, he was told a vendor’s patch had changed, and repatching was needed. “Patch panic” is common, where firms constantly expend lean resources to implement patches quickly.
The State of Virtual Patching in Enterprises Today
Across industries, virtual patching has matured into a disciplined, policy-driven process rather than an improvised safety net. Security teams now take a multi-layered approach that blends WAF or IPS rule updates, vendor-recommended mitigations, configuration hardening, and runtime protections that detect and block exploit techniques at the memory level or within application logic.
Prioritization is often tied directly to CISA’s KEV catalog, with the most urgent mitigations targeting internet-facing systems and edge devices—prime targets in today’s breach landscape. Many organizations set explicit SLAs for these mitigations, such as applying a virtual patch within hours of identification, then deploying the permanent code patch during the next approved change window. This structured approach ensures coverage without disrupting operations, particularly for systems that are business-critical, have limited maintenance windows, or run on legacy operating systems.
Yet even as many enterprises are adopting this modern approach to patch management, remediation timelines remain stubbornly long. Currently, enterprises are averaging about a month to fully patch vulnerable edge devices, and critical vulnerabilities can persist for months before being fully addressed.
As a result, temporary virtual patches often remain in place far longer than initially planned. This makes it essential for organizations to treat virtual patching as a managed, monitored control—complete with visibility into where mitigations are active, how they’re performing, and when they can be safely retired.
When combined with a preemptive cyber defense strategy, virtual patching is even more powerful. Instead of reacting to an exploit in progress, organizations can move directly from exposure discovery to immediate mitigation—closing the pre-attack window and reducing the likelihood of a successful breach.
What is Preemptive Cyber Defense
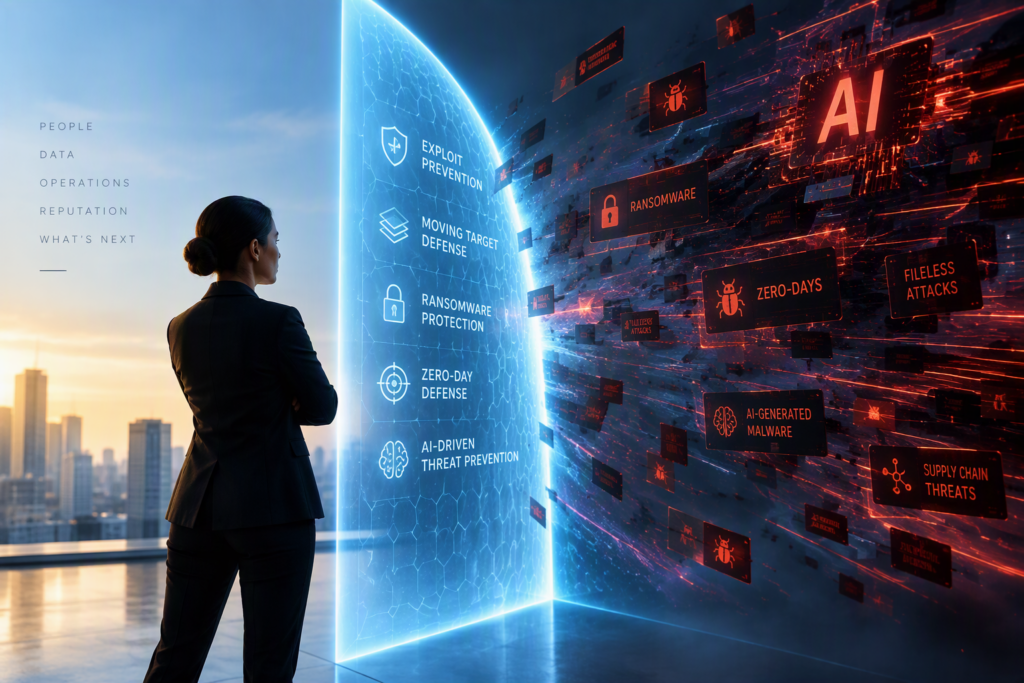
Preemptive Cyber Defense is a forward-leaning strategy that shifts cybersecurity from reaction to prevention. Rather than waiting for attacks to emerge or relying solely on detection-and-response tools, it focuses on neutralizing threats before they can materialize.
Morphisec’s pioneering Automated Moving Target Defense (AMTD) technology embodies this approach by dynamically morphing the attack surface, disrupting attacker reconnaissance and execution phases before they can gain traction.
The Role of Adaptive Exposure Management in Preemptive Defense
As part of its Anti-Ransomware Assurance Suite, Morphisec’s Adaptive Exposure Management (AEM) drives preemptive cyber defense by helping organizations identify, prioritize, and mitigate risk before patching, effectively serving as a patchless control layer by delivering:
- Software Asset Inventory: Maintains a real-time view of all installed and running applications, ensuring visibility and control over software assets.
- Vulnerability Prioritization: Continuously delivers risk-driven remediation recommendations that incorporate business context, EPSS exploit-probability scores, and CISA’s KEV list. This focuses resources on what truly matters—without waiting for patch availability.
- Security Control Validation: Confirms that protective tools—like endpoint protection agents—are properly deployed and configured. It alerts on deviations, reducing configuration drift and ensuring defenses remain effective even in complex, fast-paced environments.
- High-Risk Software Detection: Identifies software with elevated exploitation potential or misusage risk, flagging it for prioritized review or mitigation.
- Security Misconfiguration Detection: Continuously assesses endpoints for misconfigurations that may weaken security posture and provides prioritized remediation steps.
Putting It All Together: A Preemptive, Patchless Defense Posture
In a preemptive defense model, AEM becomes a shield in anticipation—detecting risky software, misconfigurations, or high-priority vulnerabilities and neutralizing them before exploit attempts occur, even if no patch is currently available.
This aligns with Gartner’s CTEM (Continuous Threat Exposure Management) directive by providing a structured, continuous approach to risk discovery, prioritization, validation, and remediation. AEM operationalizes CTEM in a patchless way, anchoring preemptive posture in real-time visibility and business-focused action.
Download the Achieving Cyber Resiliency white paper to learn how Adaptive Exposure Management can support your virtual patching efforts through adaptive and proactive strategies.
Stay up-to-date
Get the latest resources, news, and threat research delivered to your inbox.